Vulnerability Assessment & Penetration Testing
Comprehensive VAPT services to identify, assess, and remediate security vulnerabilities across your entire infrastructure before attackers can exploit them.
Explore VAPT services →SecOpsTool delivers comprehensive application security testing, vulnerability management, and endpoint protection - powered by the best tools in the industry.
From source code to production - we cover every layer of your attack surface with industry-leading tools and expert guidance.
Comprehensive VAPT services to identify, assess, and remediate security vulnerabilities across your entire infrastructure before attackers can exploit them.
Explore VAPT services →Scan source code, bytecode, and binaries for security flaws early in the SDLC - shift-left security that integrates seamlessly into your CI/CD pipeline.
Explore SAST tools and services →Identify vulnerabilities, license risks, and outdated dependencies in open-source and third-party components across your entire software supply chain.
Explore SCA and SBOM services →Test running applications for vulnerabilities like XSS, SQL injection, and authentication flaws - simulating real-world attack scenarios against your live systems.
Explore DAST tools and services →Static and dynamic analysis for iOS and Android applications - reverse engineering, runtime analysis, and compliance testing for mobile-first businesses.
Explore mobile app security →End-to-end web application security assessments covering OWASP Top 10, API security, authentication, and access control testing for modern web applications.
Explore web application security →Our team holds OSCP, CEH, CISSP, and other top-tier certifications. Decades of combined experience securing enterprises across India and globally.
Our solutions integrate with your existing DevOps pipeline in days - not months. We support all major CI/CD tools, cloud platforms, and IDEs.
We don't just find vulnerabilities - we help you fix them. Dedicated security engineers guide your team through every remediation step.
We partner with the most trusted names in cybersecurity to deliver best-in-class solutions tailored for your environment.
Vulnerability management & penetration testing tools.
VAPT · DASTOpen-source mobile security testing framework.
MAST · iOS · AndroidExpert insights, threat intelligence, and security best practices from the SecOpsTool team.
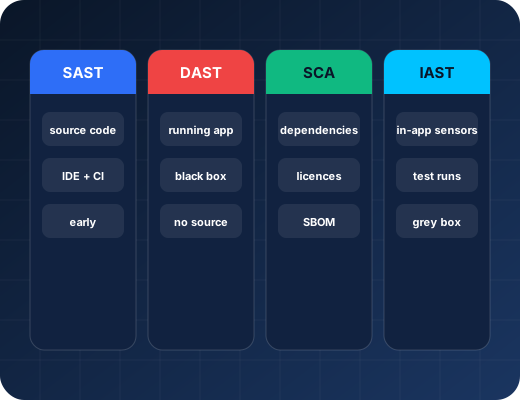 AppSec Testing
SAST, DAST, SCA and IAST test different things at different stages. See what each analyses, what it misses, and a framework for which to run first.
Read Article →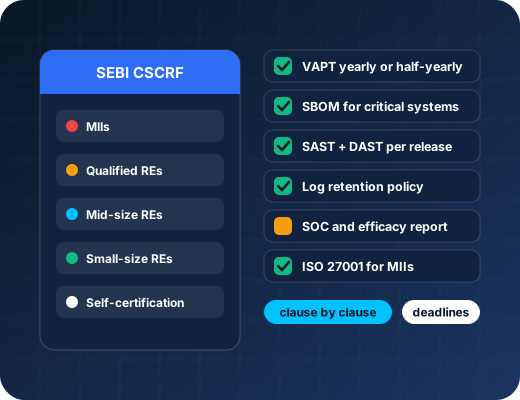 SEBI CSCRF
A clause by clause SEBI CSCRF checklist covering VAPT frequency and scope, SBOM deadlines, application security testing, log retention and SOC requirements.
Read Article →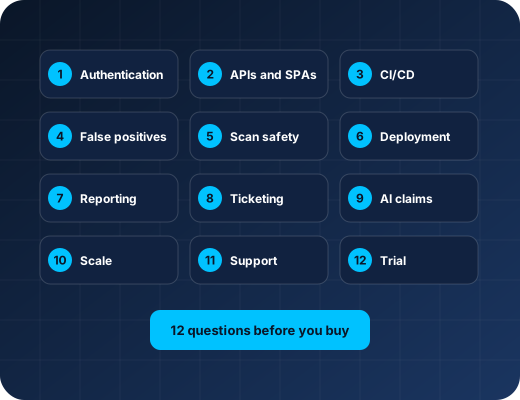 DAST
12 questions to ask DAST vendors before you buy: authentication handling, API and SPA coverage, CI/CD, false positives, scan safety and compliance reporting.
Read Article →Let our experts run a complimentary security assessment and show you exactly where your vulnerabilities lie - before attackers do.
Fill in your details and our team will reach out within 24 hours.
A VAPT combines automated vulnerability scanning with manual penetration testing to identify security weaknesses in your systems. Our certified ethical hackers simulate real-world attack scenarios to expose gaps before malicious actors can exploit them - giving you a prioritised, actionable report.
Scope varies by engagement size. A focused web application VAPT typically takes 5–10 business days. A full enterprise assessment covering infrastructure, applications, and mobile can take 3–6 weeks. We'll give you a precise timeline after the initial scoping call.
Absolutely. Our assessments are designed to map directly to major compliance frameworks including ISO 27001, SOC 2 Type II, PCI DSS, HIPAA, and GDPR. We provide detailed compliance gap reports that you can use directly in audits.
Yes - all our partnered tools (Checkmarx, Snyk, Rapid7, etc.) offer native integrations with GitHub, GitLab, Jenkins, Azure DevOps, and other popular CI/CD platforms. Our team handles the setup and configuration for you as part of the onboarding.
We serve clients across BFSI (Banking, Financial Services & Insurance), healthcare, e-commerce, SaaS, manufacturing, and government sectors. Our team understands the unique compliance and threat landscape of each industry.