Security Solutions for Every Layer
From source code to runtime, from web to mobile - SecOpsTool covers your entire attack surface with proven, enterprise-grade security solutions.
Vulnerability Assessment & Penetration Testing
Our VAPT service combines automated vulnerability scanning with hands-on ethical hacking to uncover security gaps across your entire IT landscape - before real attackers can exploit them.
- Network infrastructure & perimeter testing
- Web application penetration testing (OWASP methodology)
- API security testing & fuzzing
- Social engineering & phishing simulations
- Detailed findings report with CVSS scoring
- Remediation support & re-testing included
Tools we use: Nessus, Burp Suite, Acunetix (Invicti)
Request VAPT → VAPT services in detail →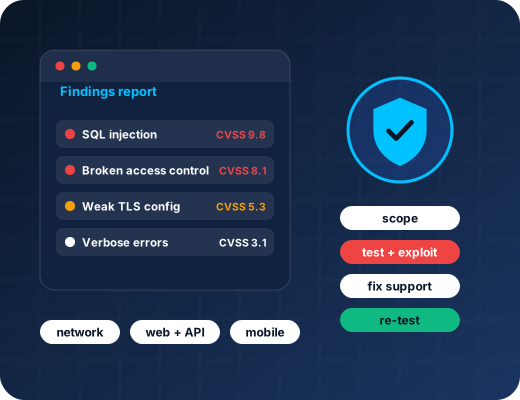
Static Application Security Testing (SAST)
Find vulnerabilities at the source - literally. SAST analyses your source code, bytecode, or binaries without executing the application, making it the ideal shift-left security tool for development teams.
- Supports 25+ programming languages (Java, Python, .NET, Node.js, etc.)
- IDE plugins for real-time developer feedback
- CI/CD pipeline integration (GitHub Actions, Jenkins, GitLab CI)
- Zero false-positive tuning & customisation
- CWE, OWASP, SANS Top 25 mapping
- Incremental scanning for fast feedback loops
Tools we supply: Klocwork, Checkmarx One, SonarQube, HCL AppScan, Understand by SciTools, O3 Security
Get SAST Demo → SAST tools and services in detail →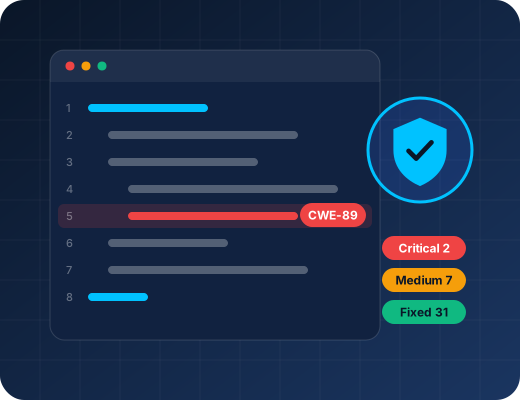
Software Composition Analysis (SCA)
Modern software is built on open-source components. SCA continuously monitors your dependencies for known CVEs, outdated libraries, and licence compliance risks across the entire software supply chain.
- Real-time CVE database monitoring & alerts
- Transitive dependency vulnerability detection
- Open-source licence compliance (GPL, MIT, Apache)
- SBOM (Software Bill of Materials) generation
- Auto-fix pull requests for vulnerable packages
- Container & Docker image scanning
Tools we supply: Mend.io, Snyk, Sonatype Lifecycle (IQ Server), Sonatype Nexus Repository, JFrog Artifactory, O3 Security
Secure Your Dependencies → SCA and SBOM services in detail →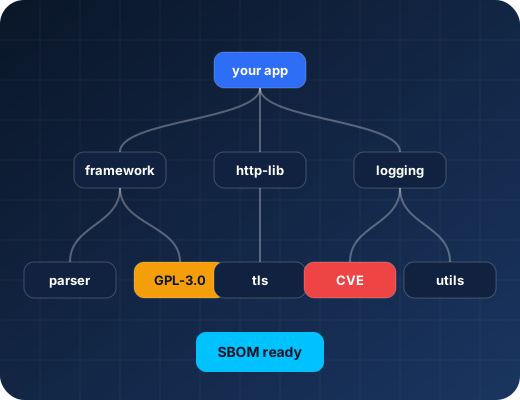
Dynamic Application Security Testing (DAST)
DAST tests your application from the outside - as an attacker would - by sending malicious inputs to a running application and analysing the responses. Perfect for finding runtime vulnerabilities SAST can't catch.
- Automated crawling & attack simulation
- SQL injection, XSS, CSRF, XXE detection
- Authentication & session management testing
- REST & GraphQL API fuzzing
- Authenticated scan support for logged-in functionality
- Integrates with staging/QA environments
Tools we supply: Acunetix (Invicti), Burp Suite, Bright Security, Sec1 DAST (Kairo), HCL AppScan, Levo.ai
Start DAST Scan → DAST tools and services in detail →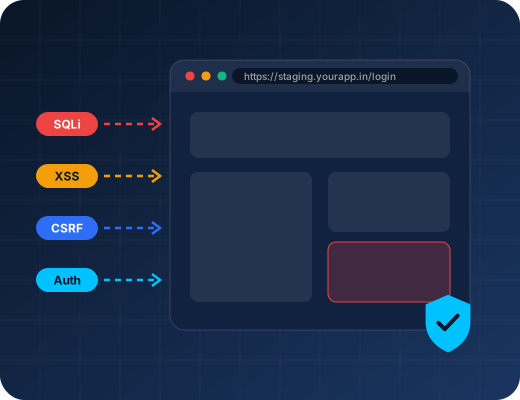
Mobile Application Security Testing
Comprehensive security assessment for iOS and Android applications - including reverse engineering, static analysis of APK/IPA files, and dynamic runtime testing on real devices and emulators.
- Android APK & iOS IPA binary analysis
- Hardcoded secrets & API key detection
- Runtime traffic interception & analysis
- OWASP Mobile Top 10 compliance checks
- SSL pinning bypass & certificate validation testing
- Insecure data storage & local database audits
Tools we supply: Appknox, Bugsmirror, Guardsquare, Protectt.ai
Audit Your Mobile App → Mobile app security in detail →
Web Application Security
Full-spectrum security assessment for web applications - from modern single-page applications to legacy monoliths. We test everything from authentication flows to business logic vulnerabilities.
- OWASP Top 10 & SANS 25 vulnerability coverage
- Business logic & access control testing
- OAuth, SAML, JWT security validation
- File upload & input validation testing
- Rate limiting & DoS resilience checks
- Detailed developer-friendly remediation guides
Tools we supply: Burp Suite, Acunetix (Invicti), Bright Security, Sec1 DAST (Kairo), Levo.ai, Ashield
Secure Your Web App → Web application security in detail →
Endpoint Security
Protect every device in your organisation - from employee laptops to servers - with next-generation endpoint detection and response (EDR) capabilities powered by AI-driven threat intelligence.
- AI-powered threat detection & response (EDR)
- Ransomware & malware protection
- Zero-trust device posture enforcement
- Behavioural analysis & anomaly detection
- Centralised management console
- Automated incident response playbooks
Tools we supply: Cymulate, Seconize, Threatcop, Nessus
Protect Your Endpoints → Endpoint security in detail →
Not Sure Which Solution You Need?
Our security consultants will assess your current posture and recommend the right mix of solutions for your specific use case and budget.
- Free 30-minute consultation with a certified expert
- Custom solution mapping to your business needs
- No-obligation proposal with transparent pricing
Talk to an Expert
Tell us about your security challenges and we'll recommend the right approach.