Security Intelligence
Cybersecurity Insights for the Modern Development Team
Deep-dive articles on SAST, SBOM, mobile security, compliance regulations, and DevSecOps - written by practitioners, not marketers. Each article links to the tools and services it discusses, with a free trial or scoping call on request.
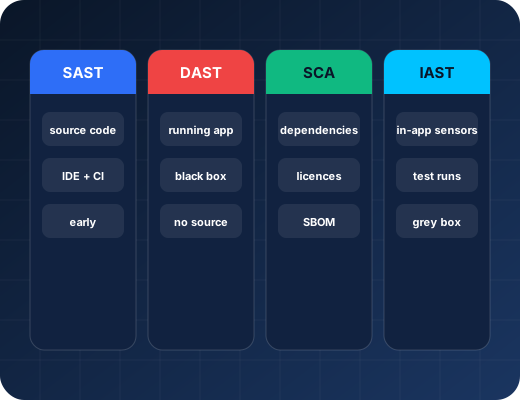
AppSec Testing Fundamentals
SAST vs DAST vs SCA vs IAST: Which Do You Need First?
SAST, DAST, SCA and IAST test different things at different stages. See what each analyses, what it misses, and a framework for which to run first.
Read Article
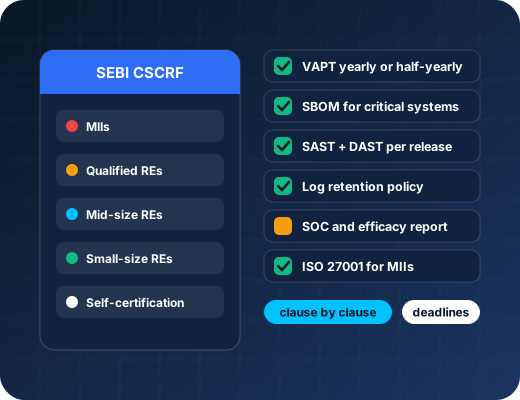
SEBI CSCRF Compliance
SEBI CSCRF Compliance Checklist: VAPT and SBOM Requirements
A clause by clause SEBI CSCRF checklist covering VAPT frequency and scope, SBOM deadlines, application security testing, log retention and SOC requirements.
Read Article
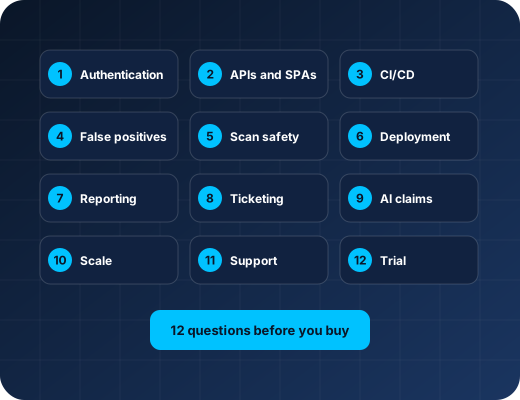
DAST & API Security
How to Choose a DAST Tool: 12 Questions to Ask Before You Buy
12 questions to ask DAST vendors before you buy: authentication handling, API and SPA coverage, CI/CD, false positives, scan safety and compliance reporting.
Read Article
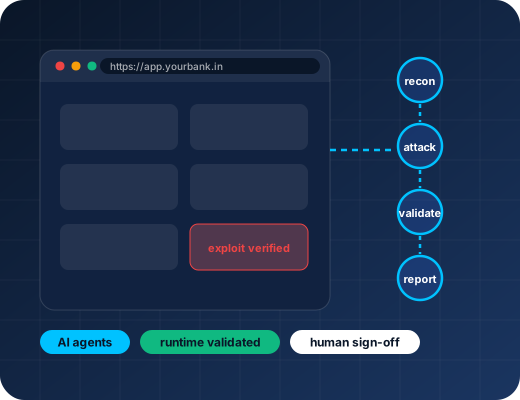
DAST & AI Security
AI DAST Explained: What Changes and What Does Not
AI DAST explained: what OWASP says conventional DAST does, and what Bright Security, Sec1, Acunetix and Burp Suite document about their own AI features.
Read Article
Artifact Repository Management
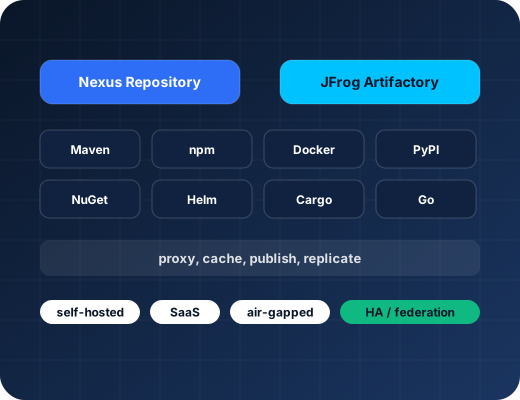
Nexus Repository vs JFrog Artifactory: How to Choose an Artifact Repository
Compare Sonatype Nexus Repository and JFrog Artifactory on editions, formats, high availability and deployment, using each vendor's own documentation.
Read Article
SCA & SBOM
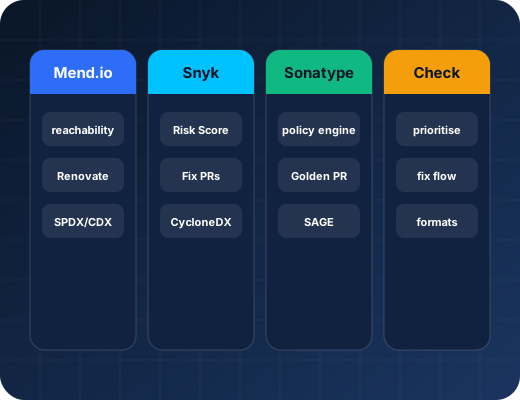
Mend vs Snyk vs Sonatype Lifecycle: an SCA Comparison
Compare Mend.io, Snyk and Sonatype Lifecycle on reachability, licence policies, SBOM formats and automated fix pull requests, using each vendor's own docs.
Read Article
Banking & NBFC Compliance
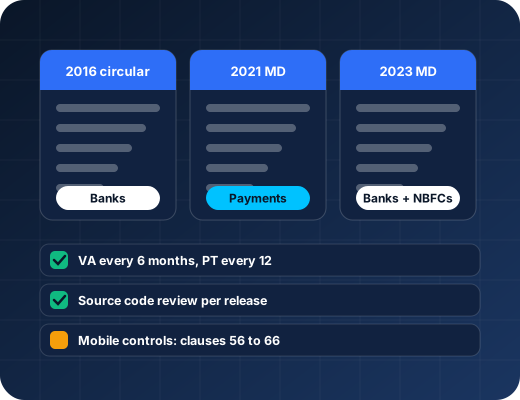
RBI Cyber Security Rules: The AppSec Controls You Must Evidence
What the RBI Cyber Security Framework, IT Governance and Digital Payment Security Master Directions require for VAPT, secure coding, mobile and API testing.
Read Article
SAST & MISRA Compliance
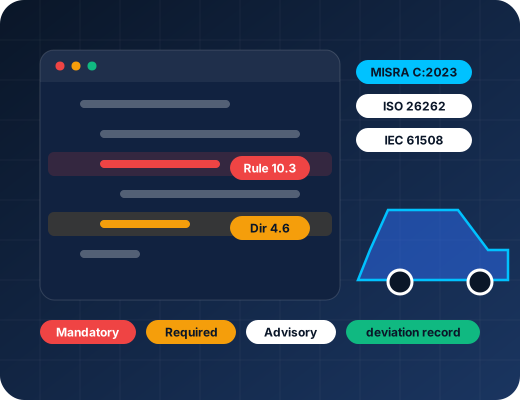
Choosing a MISRA C/C++ Static Analysis Tool for Embedded and Automotive
Compare MISRA C and MISRA C++ static analysis tools for embedded and automotive projects, covering rule coverage, deviations, tool qualification and CI fit.
Read Article
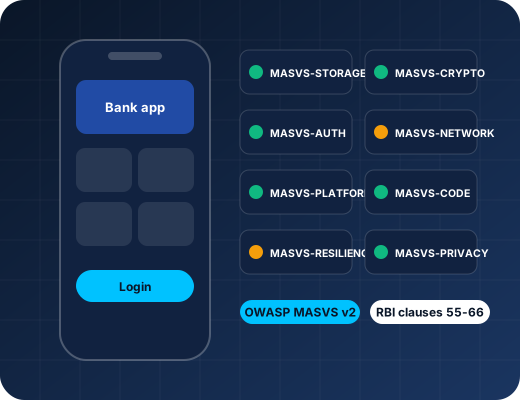
Mobile Security & Compliance
Mobile App Security Testing Checklist for Indian Banks and Fintechs
A mobile app security testing checklist for Indian banks and fintechs, mapping OWASP MASVS v2 control groups to RBI's Digital Payment Security Controls clauses.
Read Article
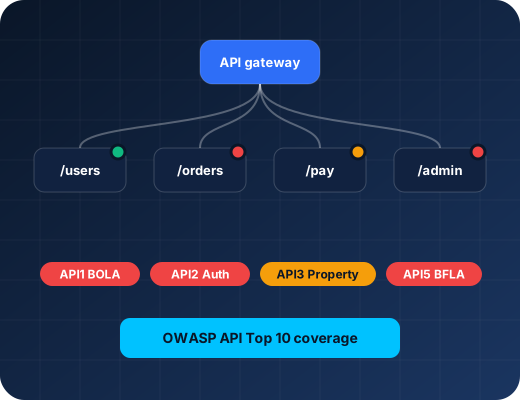
DAST & API Security
API Security Testing: Covering the OWASP API Top 10
A category by category guide to the OWASP API Security Top 10 (2023), how each risk is tested, and how discovery, schema scanning and CI/CD gates fit together.
Read Article
SAST · Embedded Security
Why Every Embedded Software Team Needs SAST: The Klocwork Advantage
Buffer overflows in CAN bus parsers. Race conditions in braking controllers. These aren't theoretical risks - they're what SAST finds before your code ships. A deep dive into Klocwork for C/C++ embedded systems.
Read Article
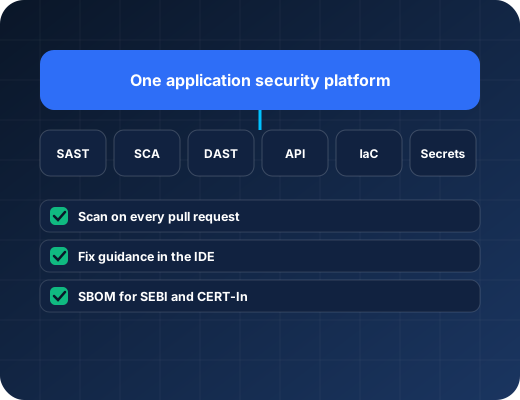
Application Security · DevSecOps
From Code to Cloud: Building a Complete Application Security Programme with Checkmarx
Many breaches now start with an application vulnerability. Learn how Checkmarx One unifies SAST, SCA, DAST, and API security in one platform - and how to implement DevSecOps that moves at developer speed.
Read Article
SCA · SBOM · SEBI Compliance
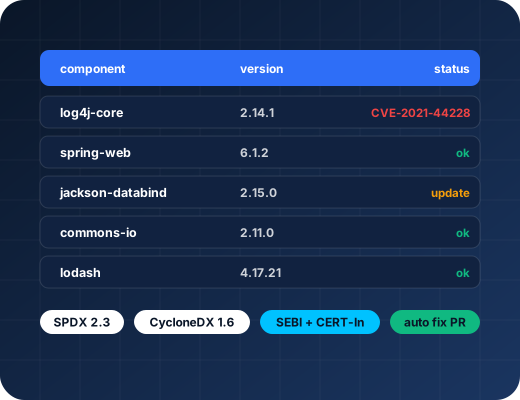
SBOM Compliance for SEBI & CERT-In: How Mend.io Automates Software Supply Chain Governance
SEBI CSCRF requires financial institutions to know every software component in their stack. Manual SBOM creation is impossible at scale. Here's how Mend.io automates it - with real SBOM output screenshots.
Read Article
CBOM · SEBI · Post-Quantum
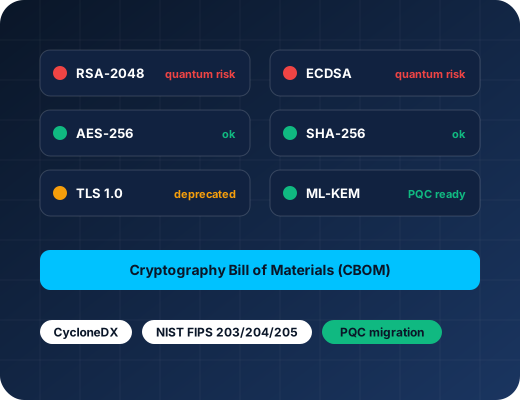
CBOM: India's Next Regulatory Frontier - How O3 Security Helps Financial Firms Comply
SBOM tells you what's running. CBOM tells you how it's protected. With RSA vulnerable to quantum computers and SEBI demanding cryptographic governance, Indian fintechs must act now.
Read Article
Unit Testing · DO-178C · ISO 26262
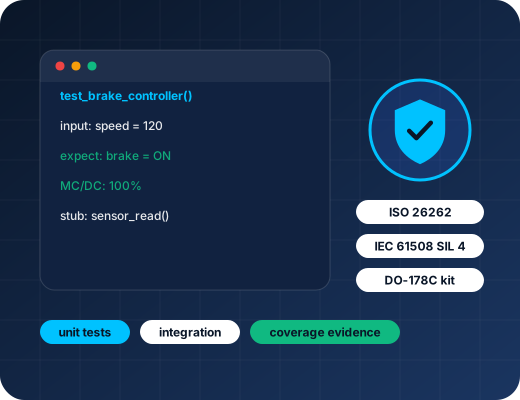
Stop Shipping Untested Code: How Cantata Automates Unit Testing for Safety-Critical C/C++
DO-178C demands 100% MC/DC coverage. ISO 26262 ASIL-D requires full branch coverage. Manual test creation can't scale to these requirements. Cantata automates stub generation, coverage, and traceability.
Read Article
Mobile RASP · Fintech Security
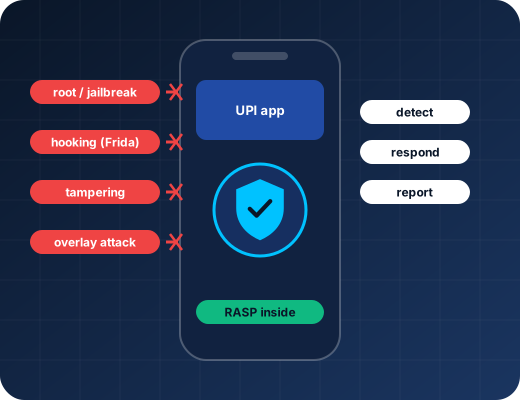
Is Your Mobile App a Ticking Time Bomb? Why Runtime Protection is Non-Negotiable for Fintech
Frida hooking, app repackaging, MITM attacks - these happen in your users' hands every day. Static testing doesn't protect against runtime attacks. Bugsmirror RASP does - from inside the app itself.
Read Article
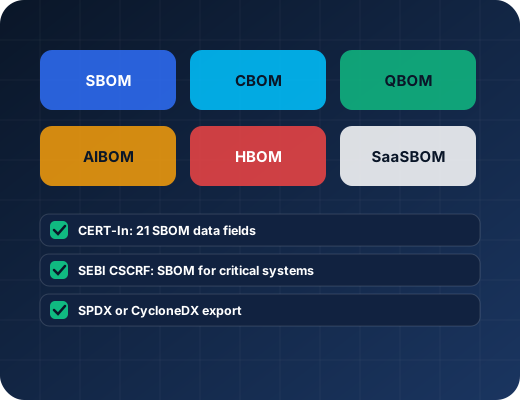
BOM Compliance · SEBI · CERT-In
Is Your Organisation BOM-Ready? How O3 Security's Complete BOM Suite Satisfies SEBI, CERT-In & RBI
SBOM is just one of six BOMs Indian regulations now require. CERT-In mandates 21 attributes per component. SEBI CSCRF requires supply chain transparency. Discover how O3 Security covers them all.
Read Article
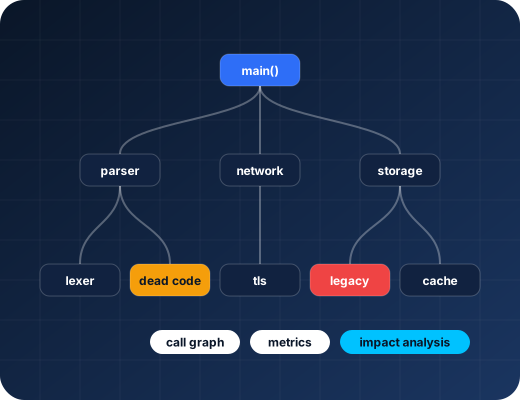
Code Analysis · Understand · SciTools
Your Codebase Is a Black Box - Here's How to See Inside It: Understand by SciTools
New developer, legacy code, no documentation - sound familiar? Understand by SciTools gives you instant architecture visualisation, dependency maps, and 800+ code metrics. Stop guessing, start knowing.
Read Article
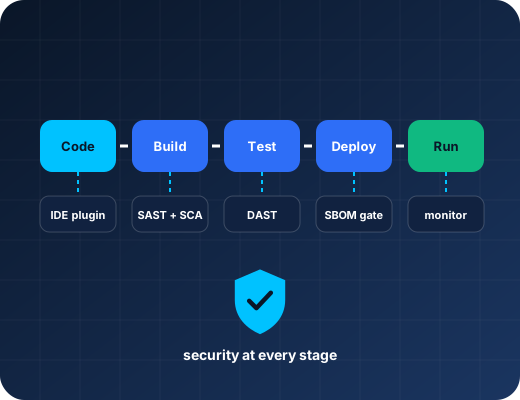
DevSecOps · CI/CD · Enterprise Security
From Zero to Enterprise-Grade DevSecOps: Building Security Into Every Stage of Your Pipeline
Stop treating security as a phase after development. This guide shows you exactly how to integrate SAST, SCA, DAST, secrets detection, and SBOM generation into your CI/CD pipeline - from IDE to production.
Read Article
Weekly Security Intelligence
Stay Ahead of the Threat - Subscribe Free
Vulnerability alerts, SEBI/CERT-In compliance updates, new tool reviews, and expert guides - delivered every week.
No spam. Unsubscribe any time.