A large share of modern breaches now start with a vulnerability in an application - not the network perimeter, not the firewall. The application. Application security is no longer a specialist discipline that lives in a separate team. It has become the defining discipline of modern software engineering.
Yet most organisations still treat AppSec as a phase that happens after development - a penetration test before a major release, a compliance checkbox. This approach is slow, expensive, and broken. Checkmarx was built to fix it.
The Cost of Late-Stage Security
Vulnerabilities caught in production are consistently more disruptive and costly to fix than the same issue caught during development, because a production fix means an emergency patch and incident response instead of a code review comment. Security-first organisations that catch issues early avoid this cost while their peers scramble after the fact.
The core problem: When security testing happens at the end of the SDLC, it creates friction, delays releases, and produces a waterfall of findings that overwhelms developers. DevSecOps is the answer - but only if your tools can move at developer speed.
What is Checkmarx One?
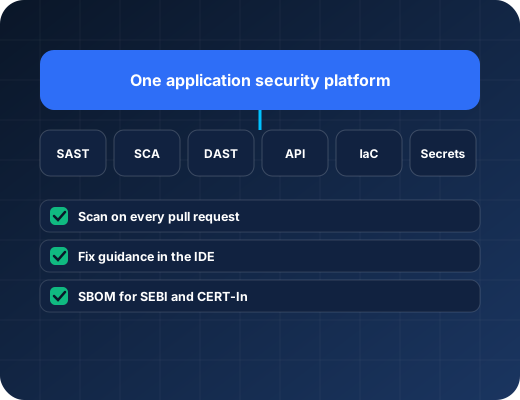
Checkmarx One is a unified, cloud-native Application Security Platform combining SAST, SCA, DAST, API security, IaC security, and container security in a single platform. The key insight: vulnerabilities don't live in isolation. A flaw in your code, combined with an outdated dependency, exposed through an unprotected API - that's how real attacks happen. Checkmarx Fusion correlates findings across all dimensions to surface real risk, not theoretical noise.
Get a 14-day free trial with expert onboarding from SecOpsTool, or compare it with the alternatives first.
SAST: Finding Bugs in 30+ Languages at Developer Speed
Checkmarx SAST supports a wide range of programming languages, including Java, .NET, Python, JavaScript, TypeScript, Go, PHP, Kotlin, and Swift. Incremental scanning analyses only the code that changed on a pull request instead of rescanning the whole repository, so scans complete faster than a full scan.
// Language: Java | CWE-89 | Severity: HIGH
// Vulnerable code:
String query = "SELECT * FROM users WHERE id = " + userId;
stmt.executeQuery(query); // ← CX: userId flows unsanitised into SQL
// Data flow: HTTP param → userId → query → executeQuery()
// Fix: Use PreparedStatement with parameterised queries
SCA: Open Source Risk and SBOM Generation
Modern applications are around 80% open-source code, according to Checkmarx. Checkmarx SCA scans all dependencies across package managers (Maven, npm, pip, NuGet, Go modules) against the latest CVE databases. It generates SBOM reports in SPDX and CycloneDX formats for SEBI CSCRF, CERT-In, and supply chain compliance requirements. Auto-fix pull requests recommend updated package versions to help remediate vulnerable dependencies.
API Security: The Attack Surface You Probably Aren't Testing
APIs are a growing attack surface. OWASP's API Security Top 10 documents the ten most critical API security risks. Checkmarx discovers and tests APIs automatically, including shadow and zombie APIs that exist outside your known inventory but are still reachable by attackers.
🔒 Try Checkmarx Free for 14 Days
Full Checkmarx One platform access - SAST, SCA, API security. Expert onboarding, CI/CD integration support, and a post-trial security assessment included.
Start My Free 14-Day Trial →Integrating Checkmarx into Your CI/CD Pipeline
- GitHub Actions / GitLab CI: Scan runs automatically on every pull request; results posted as inline code review comments
- Jenkins: Native Checkmarx plugin with configurable quality gates - fail builds on critical findings
- Jira / Azure DevOps: Auto-create security tickets for critical findings with full triage data and remediation guidance
- IDE plugins: IntelliJ, VS Code, Eclipse - developers see findings as they code, not after they commit
Building Maturity: From Tool to Programme
Checkmarx isn't just a scanner - it's the foundation of an AppSec programme. The platform tracks your security posture over time, measures team-level performance, and produces the metrics that CISOs need to demonstrate programme ROI to the board. Start with SAST, add SCA as open-source risk grows, layer in API security as your API surface expands. The platform scales with your maturity.
The organisations that win at application security aren't the ones with the biggest security teams. They're the ones that build security into the development process itself - making every developer a security stakeholder. Checkmarx makes that possible at enterprise scale.
Sources
Primary documents this article is based on. Product statements and regulatory clauses above were checked against these pages.
- Checkmarx Fusion / Risk Orchestration
- Checkmarx SAST - Supported Languages and Frameworks
- Checkmarx SAST Scanner docs (incremental scanning)
- Checkmarx SCA - installing supported package managers
- Checkmarx SBOM product page (SPDX/CycloneDX export)
- Checkmarx - open-source share of the average codebase
- Checkmarx API Security product page (shadow/zombie APIs)
- SEBI CSCRF circular (SBOM mandate, control GV.SC.S5)
- CERT-In Technical Guidelines on SBOM v2.0 (SPDX/CycloneDX formats)
- OWASP API Security Top 10 (2023 edition)
Further Reading
- Checkmarx: features, use cases and free trial
- Checkmarx vs Fortify: detailed comparison
- SonarQube vs Checkmarx: detailed comparison
- Veracode vs Checkmarx: detailed comparison
- From Zero to Enterprise-Grade DevSecOps: Building Security Into Every Stage of Your Pipeline
- OWASP Top 10 (external)
- CWE Top 25 Most Dangerous Software Weaknesses (external)