Web Application Security Testing Services in India
Web applications are the most exposed part of most organisations: they face the internet, change every sprint and hold the data attackers want. A web application security assessment combines automated scanning with manual testing to find what scanners alone miss, especially access control and business logic flaws.
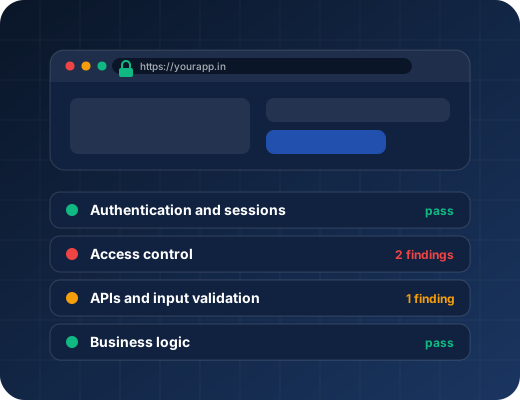
How SecOpsTool Delivers Web App Security
SecOpsTool tests everything from modern single-page applications and APIs to legacy monoliths, and gives your developers a report they can act on.
Standards and Frameworks We Map To
What Is Covered
- OWASP Top 10 and SANS 25 vulnerability coverage
- Business logic and access control testing
- OAuth, SAML and JWT security validation
- File upload and input validation testing
- Rate limiting and denial-of-service resilience checks
- Developer-friendly remediation guides
From First Call to Working Security Control
- 1
Scoping call
We agree the applications, user roles, environments and testing windows, and whether testing is black-box or grey-box.
- 2
Automated baseline
Scanners map the attack surface and pick up known vulnerability classes quickly.
- 3
Manual testing
Testers work through authentication, session handling, access control and business logic, where the serious findings usually are.
- 4
Report
Each finding comes with severity, evidence, reproduction steps and a recommended fix, prioritised so your team knows where to start.
- 5
Fix support and re-test
We answer developer questions during remediation and re-test the fixes.
Web App Security Tools We Supply and Support
Licences, 14-day trials, onboarding and integration support from SecOpsTool.
Comparisons and Guides
Talk to a Web App Security Specialist
Tell us about your applications and goals. We will recommend the right approach and tools, and arrange a free trial where one applies.
- No-cost initial review of your requirements
- Tool shortlist matched to your stack and compliance needs
- Response within 24 hours
Get Your Free Assessment
Fill in your details and our team will reach out within 24 hours.
Web App Security: Frequently Asked Questions
Scanners are good at known vulnerability patterns. They are weak at access control, multi-step workflows and business logic, which is where many serious issues sit. Manual testing covers that gap.
A focused web application assessment typically takes 5 to 10 business days, depending on size and the number of user roles. We confirm the timeline after the scoping call.
A report with an executive summary, prioritised findings, evidence and reproduction steps, and fix recommendations, followed by a re-test of the fixes.
Yes. Findings are mapped to frameworks such as OWASP Top 10, PCI DSS and ISO 27001, so the report can support your audits.