DAST Tools and Dynamic Application Security Testing in India
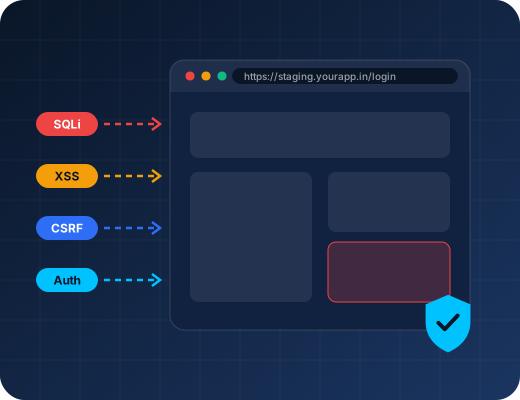
Dynamic Application Security Testing (DAST) tests a running application from the outside, the way an attacker would. The scanner crawls your web application or API, sends malicious inputs and analyses the responses to find flaws that only show up at runtime.
How SecOpsTool Delivers DAST
SecOpsTool helps you pick the right scanner, configure authenticated scans that reach the pages behind login, and run DAST automatically against staging so issues are caught before every release.
Standards and Frameworks We Map To
What Is Covered
- Automated crawling and attack simulation
- SQL injection, XSS, CSRF and XXE detection
- Authentication and session management testing
- REST and GraphQL API testing
- Authenticated scans for logged-in functionality
- Integration with staging and QA environments
From First Call to Working Security Control
- 1
Target and scope
We agree the applications, APIs and environments in scope, and the scan windows that suit each one.
- 2
Authenticated scan setup
Login sequences, tokens and roles are configured so the scanner tests the functionality behind the login page, not just the public pages.
- 3
Scan and verify
Automated scanning is followed by verification of the findings, so your developers do not chase false alarms.
- 4
Pipeline automation
Scans are triggered from CI/CD against staging, with results pushed to your issue tracker.
- 5
Fix and re-scan
Developers receive reproduction steps and fix guidance, and fixed issues are confirmed by a re-scan.
DAST Tools We Supply and Support
Licences, 14-day trials, onboarding and integration support from SecOpsTool.
Comparisons and Guides
Talk to a DAST Specialist
Tell us about your applications and goals. We will recommend the right approach and tools, and arrange a free trial where one applies.
- No-cost initial review of your requirements
- Tool shortlist matched to your stack and compliance needs
- Response within 24 hours
Get Your Free Assessment
Fill in your details and our team will reach out within 24 hours.
DAST: Frequently Asked Questions
Yes. Authenticated scanning is essential, because most business functionality sits behind the login page. We configure login sequences, session handling and user roles as part of the setup.
We recommend scanning a staging environment that mirrors production. Production scans are possible with safe scan profiles and agreed time windows, but active attack payloads can create test data or load.
Yes. Modern scanners import OpenAPI or Postman definitions, or discover APIs from traffic, and test REST and GraphQL endpoints for injection, broken authentication and authorisation flaws.
Yes. We arrange a 14-day trial of the shortlisted scanner and help you run the first authenticated scan.