Software Composition Analysis (SCA) and SBOM Services in India
Most modern applications are largely open-source code that your team did not write. Software Composition Analysis (SCA) inventories every direct and transitive dependency, matches it against vulnerability and licence databases, and tells you what to upgrade first.
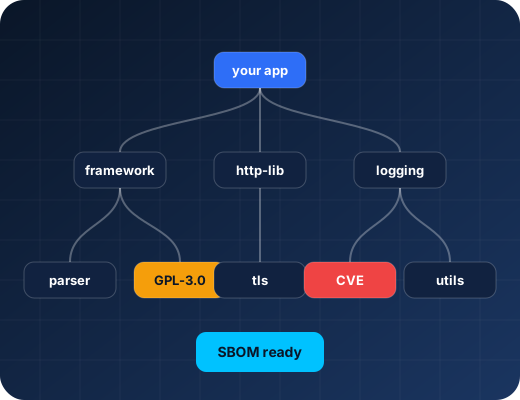
How SecOpsTool Delivers SCA
For regulated Indian organisations, SCA is also how you produce the Software Bill of Materials (SBOM) referred to in SEBI CSCRF and the CERT-In SBOM guidelines. SecOpsTool supplies and integrates the tooling and helps you turn SBOM generation into a repeatable process.
Standards and Frameworks We Map To
What Is Covered
- Continuous CVE monitoring and alerts
- Transitive dependency vulnerability detection
- Open-source licence compliance (GPL, MIT, Apache)
- SBOM generation in CycloneDX and SPDX formats
- Automated fix pull requests for vulnerable packages
- Container and Docker image scanning
From First Call to Working Security Control
- 1
Inventory
Every repository, package manager and container image is scanned to build a complete list of direct and transitive components.
- 2
Risk triage
Findings are prioritised by severity, exploit availability and whether a fixed version exists, so teams start with what matters.
- 3
Licence policy
Licence obligations are checked against a policy agreed with your legal team, and violations are flagged before release.
- 4
SBOM generation
SBOMs are produced automatically on every build in CycloneDX or SPDX format and stored for audit.
- 5
Continuous monitoring
New vulnerabilities in components you already ship raise alerts and, where supported, automated fix pull requests.
SCA Tools We Supply and Support
Licences, 14-day trials, onboarding and integration support from SecOpsTool.
Comparisons and Guides
Talk to a SCA Specialist
Tell us about your applications and goals. We will recommend the right approach and tools, and arrange a free trial where one applies.
- No-cost initial review of your requirements
- Tool shortlist matched to your stack and compliance needs
- Response within 24 hours
Get Your Free Assessment
Fill in your details and our team will reach out within 24 hours.
SCA: Frequently Asked Questions
A Software Bill of Materials is a machine-readable list of every component inside an application, with versions, suppliers and licences. It lets you answer quickly whether you are affected when a new vulnerability such as Log4Shell is announced.
SEBI's CSCRF asks regulated entities to maintain SBOMs for critical systems, and CERT-In has published technical guidelines on SBOM. Requirements differ by sector, so check the circulars that apply to you. We can help you map them to a practical process.
SAST analyses the code your team writes. SCA analyses the third-party and open-source components you depend on. They find different problems, and most programmes need both.
Yes. We arrange a 14-day trial of the shortlisted tool and help you scan your own repositories and generate a first SBOM.