Mobile Application Security Testing and RASP in India
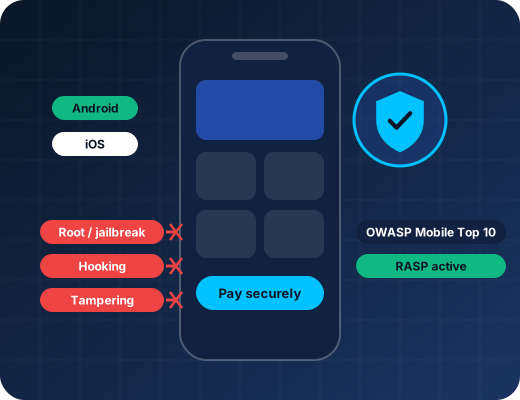
A mobile app runs on devices you do not control. Attackers can decompile it, hook into it at runtime, run it on rooted or jailbroken phones and intercept its traffic. Mobile application security combines testing, to find weaknesses before release, with runtime protection, to defend the app once it is in the wild.
How SecOpsTool Delivers Mobile App Security
SecOpsTool supplies and integrates mobile application security testing (MAST) and Runtime Application Self-Protection (RASP) tools, with a focus on the banking, fintech and payments apps that Indian regulators look at most closely.
Standards and Frameworks We Map To
What Is Covered
- Android APK and iOS IPA binary analysis
- Hardcoded secrets and API key detection
- Runtime traffic interception and analysis
- OWASP Mobile Top 10 checks
- SSL pinning and certificate validation testing
- Insecure data storage and local database audits
From First Call to Working Security Control
- 1
Static analysis of the binary
The APK or IPA is analysed for hardcoded secrets, weak cryptography, insecure storage and risky permissions. Source code is not required.
- 2
Dynamic testing on real devices
The app is exercised on devices and emulators while traffic, storage and runtime behaviour are inspected.
- 3
API and backend testing
The APIs behind the app are tested for authentication, authorisation and injection flaws.
- 4
Runtime protection
Where the risk justifies it, RASP and code hardening are added to detect rooting, hooking, tampering and repackaging.
- 5
Release gate
Testing is wired into the mobile CI/CD pipeline, so every build is checked before it reaches the app stores.
Mobile App Security Tools We Supply and Support
Licences, 14-day trials, onboarding and integration support from SecOpsTool.
Comparisons and Guides
Talk to a Mobile App Security Specialist
Tell us about your applications and goals. We will recommend the right approach and tools, and arrange a free trial where one applies.
- No-cost initial review of your requirements
- Tool shortlist matched to your stack and compliance needs
- Response within 24 hours
Get Your Free Assessment
Fill in your details and our team will reach out within 24 hours.
Mobile App Security: Frequently Asked Questions
MAST is testing: it finds vulnerabilities in the app before release. RASP is protection: it is built into the app and detects or blocks attacks such as hooking, tampering and running on rooted devices at runtime. Testing reduces the weaknesses, RASP defends what remains.
Not for most tests. Binary analysis works on the compiled APK or IPA. Source code helps for deeper review, but it is optional.
Yes. The tools we supply cover both platforms, including apps built with cross-platform frameworks.
Yes. We arrange a 14-day trial and help you scan your own app build.